SolutionsIntelligence
Covert network flows
Visibility into covert network traffic on a global scale. Observe adversary activity across Tor, residential proxies and ORB networks, where traditional telemetry cannot reach.
Available exclusively to vetted government partners
Beyond the perimeter
Your perimeter is not the limit of your visibility
Hostile operations rarely connect straight from home. They are routed through infrastructure in third countries first, so by the time traffic reaches you it arrives from somewhere unremarkable. Covert network flows watches those hops, so the path behind the connection becomes visible.
Africa
- Main sector targeted
- Financial services
- Unique targets, past 24 h
- 1.3M
Log distribution
Connections, past 24 h
- TOR48M
- FLAMEPROXIES12M
- DATAIMPULSE7.0M
- SOAX3.0M
All regions
Hover over a region, or focus it, for its figures.
- Main sector targeted
- Government and defence
- Unique targets, past 24 h
- 51M
Log distribution
Connections, past 24 h
- TOR1.0B
- BRIGHTDATA255M
- DECODO210M
- IPROYAL130M
Asia
- Main sector targeted
- Telecommunications
- Unique targets, past 24 h
- 11M
Log distribution
Connections, past 24 h
- TOR220M
- IPROYAL130M
- BOTTINGTOOLS50M
- OXYLABS30M
Europe
- Main sector targeted
- Energy and utilities
- Unique targets, past 24 h
- 18M
Log distribution
Connections, past 24 h
- TOR380M
- DECODO140M
- SOAX80M
- FLOPPYDATA40M
North America
- Main sector targeted
- Water utilities
- Unique targets, past 24 h
- 14M
Log distribution
Connections, past 24 h
- BRIGHTDATA230M
- TOR190M
- EXPRESSVPN70M
- DATAIMPULSE30M
Oceania
- Main sector targeted
- Defence suppliers
- Unique targets, past 24 h
- 4.2M
Log distribution
Connections, past 24 h
- TOR120M
- OXYLABS45M
- BRIGHTDATA25M
- FLAMEPROXIES10M
South America
- Main sector targeted
- Government ministries
- Unique targets, past 24 h
- 2.9M
Log distribution
Connections, past 24 h
- DECODO70M
- TOR50M
- FLOPPYDATA14M
- EXPRESSVPN6.0M
- Originating threat actor
- Anonymising IP monitored by Webscout
Illustrative. Actors, routes, monitored IPs and region statistics are examples, not observed traffic or sensor locations. Grey connections run through anonymising IPs that Webscout does not monitor, so they stay invisible to you. Provider names belong to their respective owners. Land outlines: Natural Earth.
What it enables
Unique visibility into the infrastructure that enables modern threats
01
Trace connections to their origin
Follow anonymised connections back through the hops to where they started.
02
See attacks beyond your perimeter
Spot operations that never touch your network, on infrastructure your sensors cannot see.
03
See through the attacker’s eyes
Observe operations from the adversary’s side of the connection: targets, tools and timing.
04
Track adversary movements
See how adversaries move across covert infrastructure, and where they go next.
05
Attribute activity
Tie activity to specific threat actors and the tooling they use.
06
Find who is targeting you
Search the flows for your own address ranges to see who reaches them through covert networks.
07
See trends first
Spot emerging exploitation trends before they appear in public reporting.
08
Group encrypted sessions
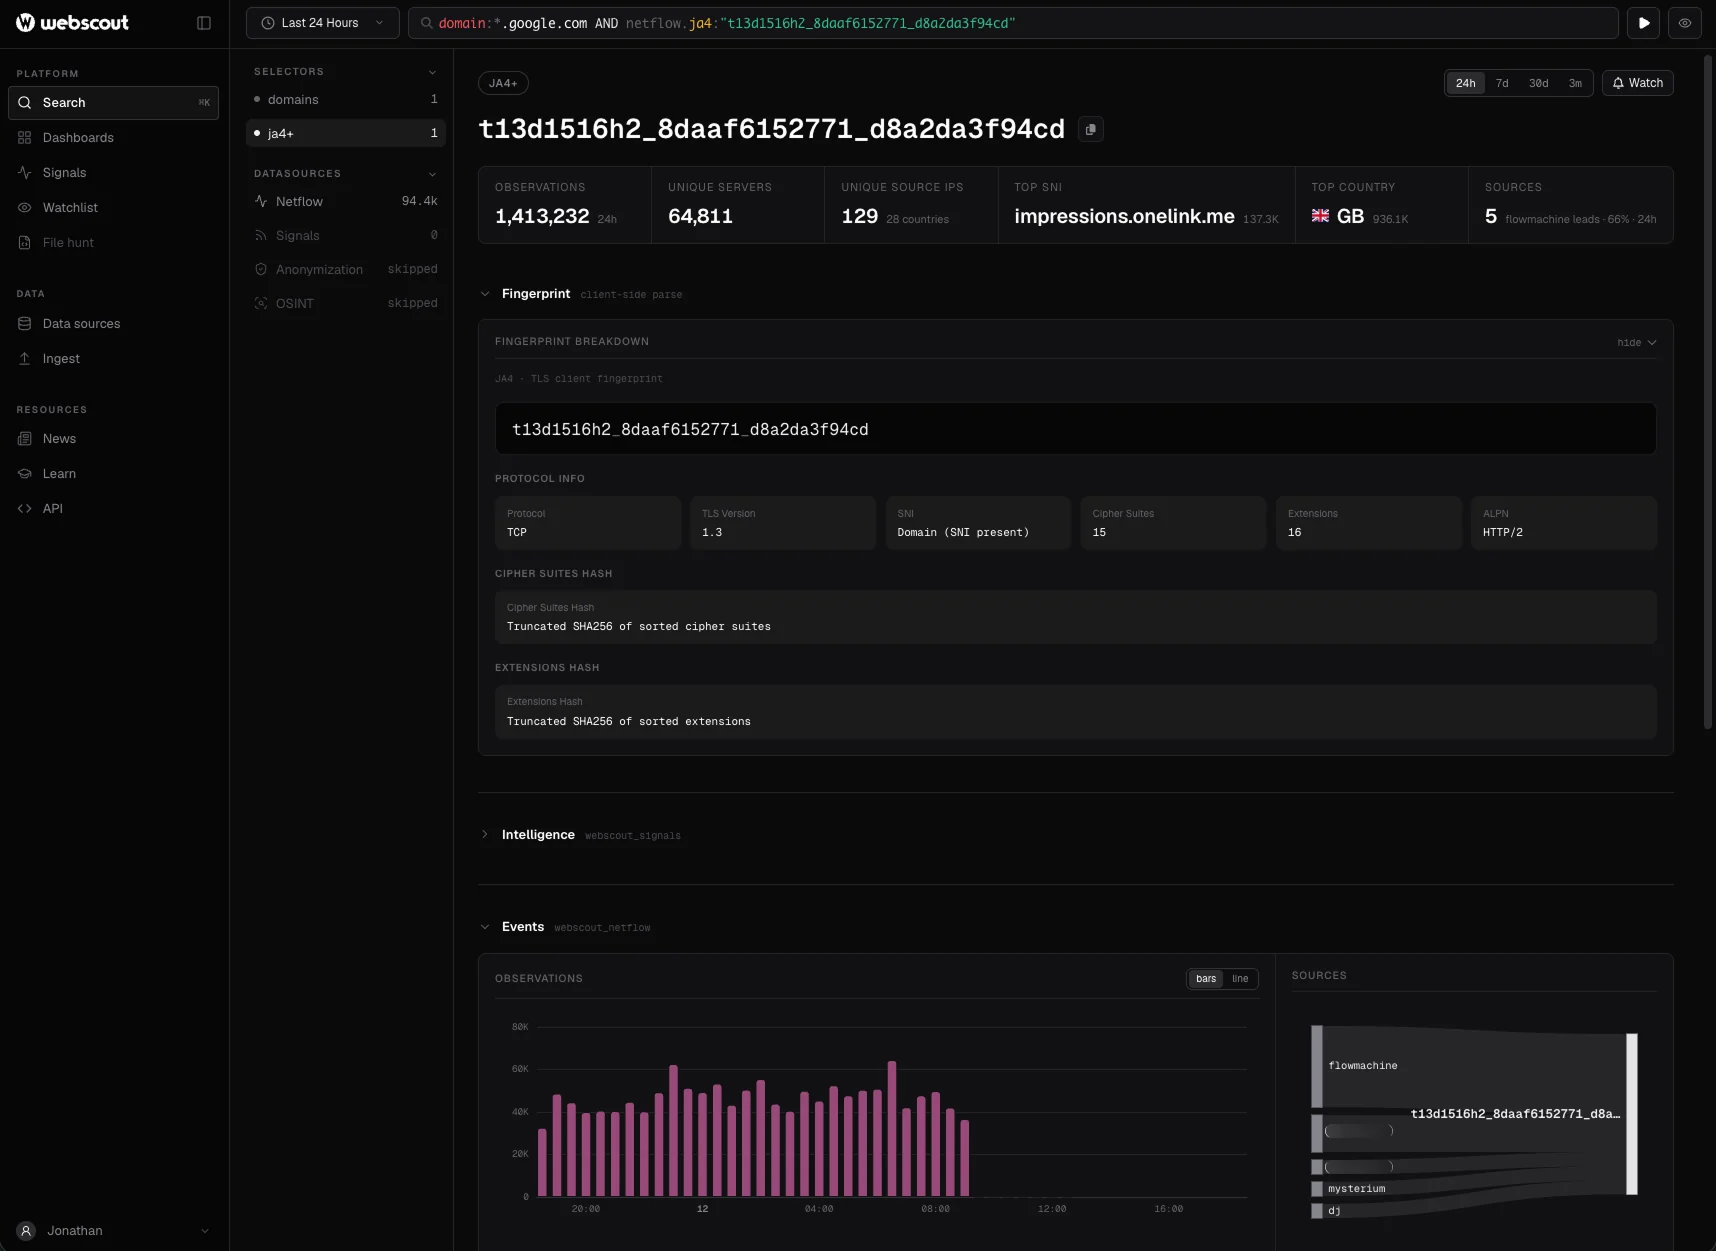
Flows carry JA4+ fingerprints, so encrypted sessions can be grouped and tracked without decryption.
In the platform
Hunt in the platform, or take the flows home
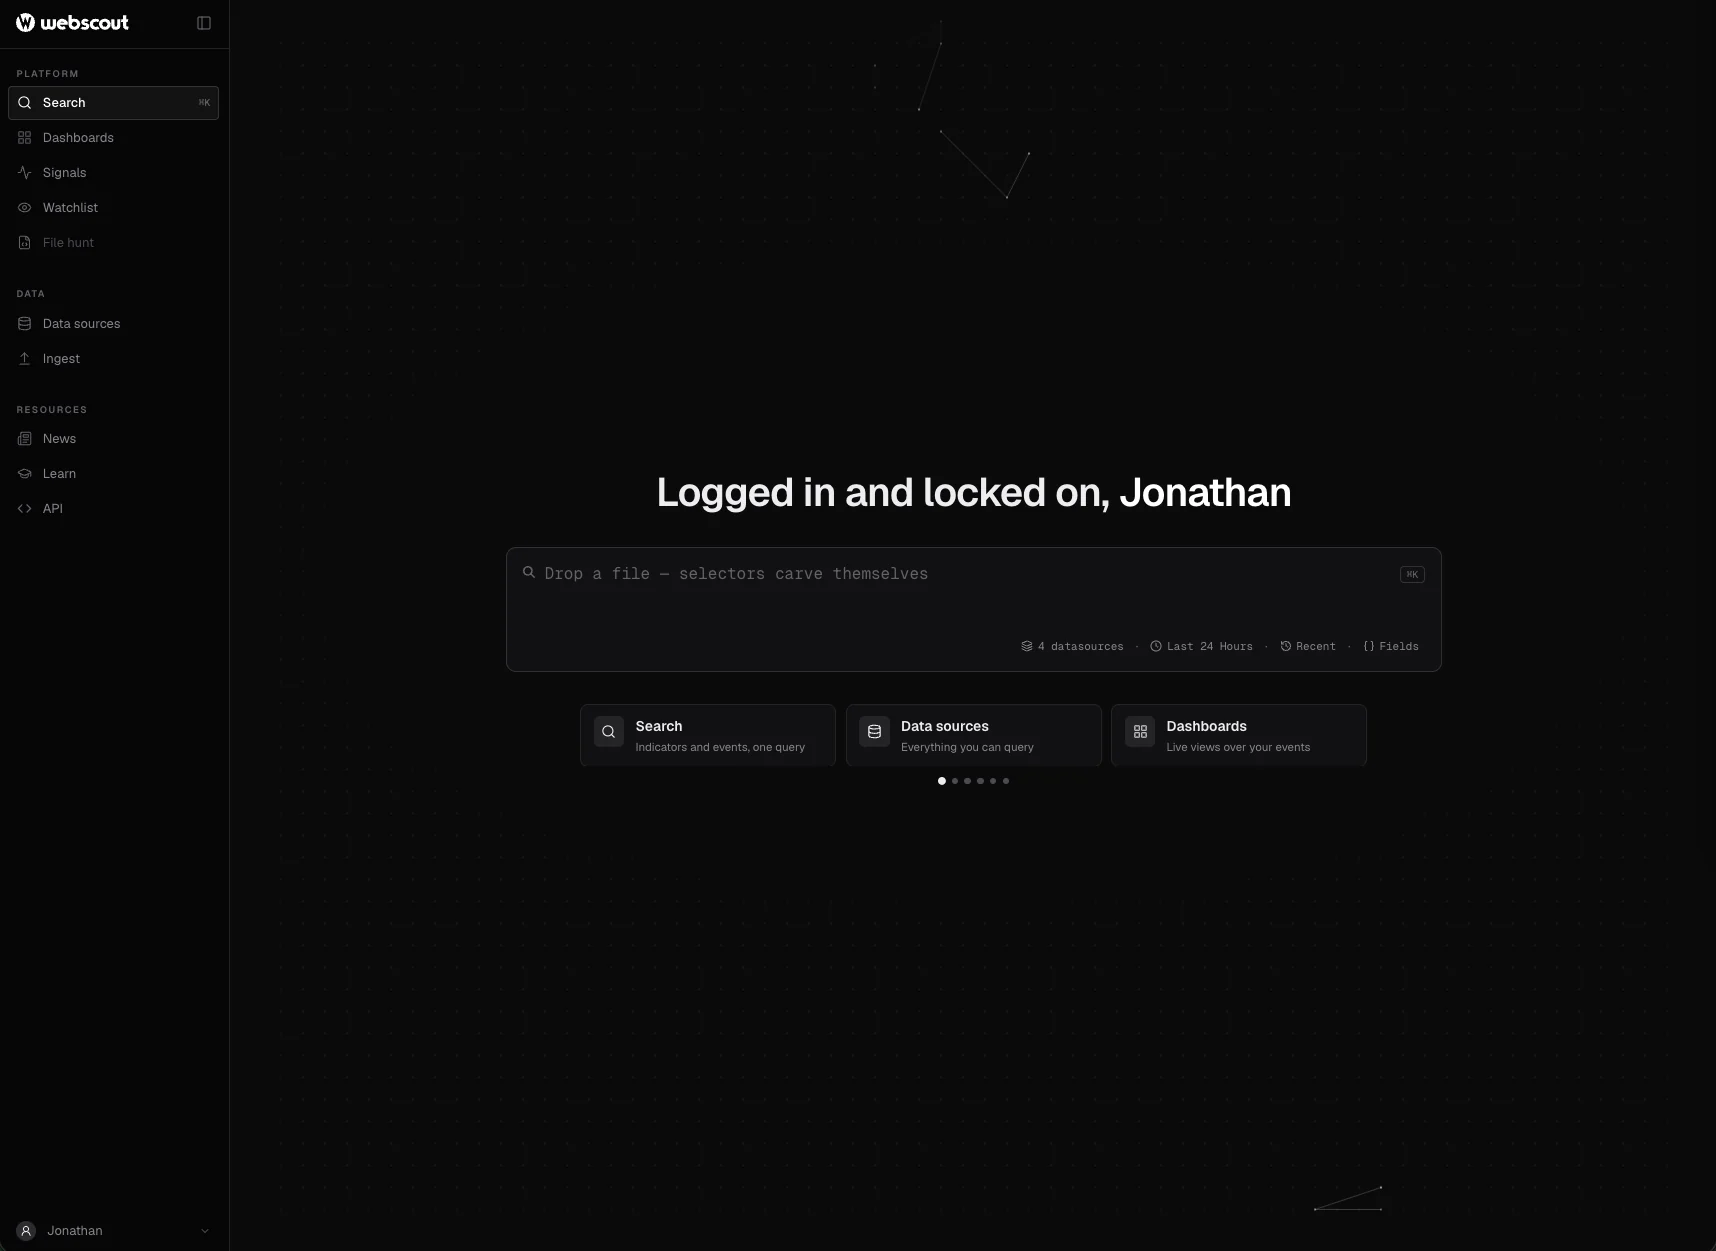
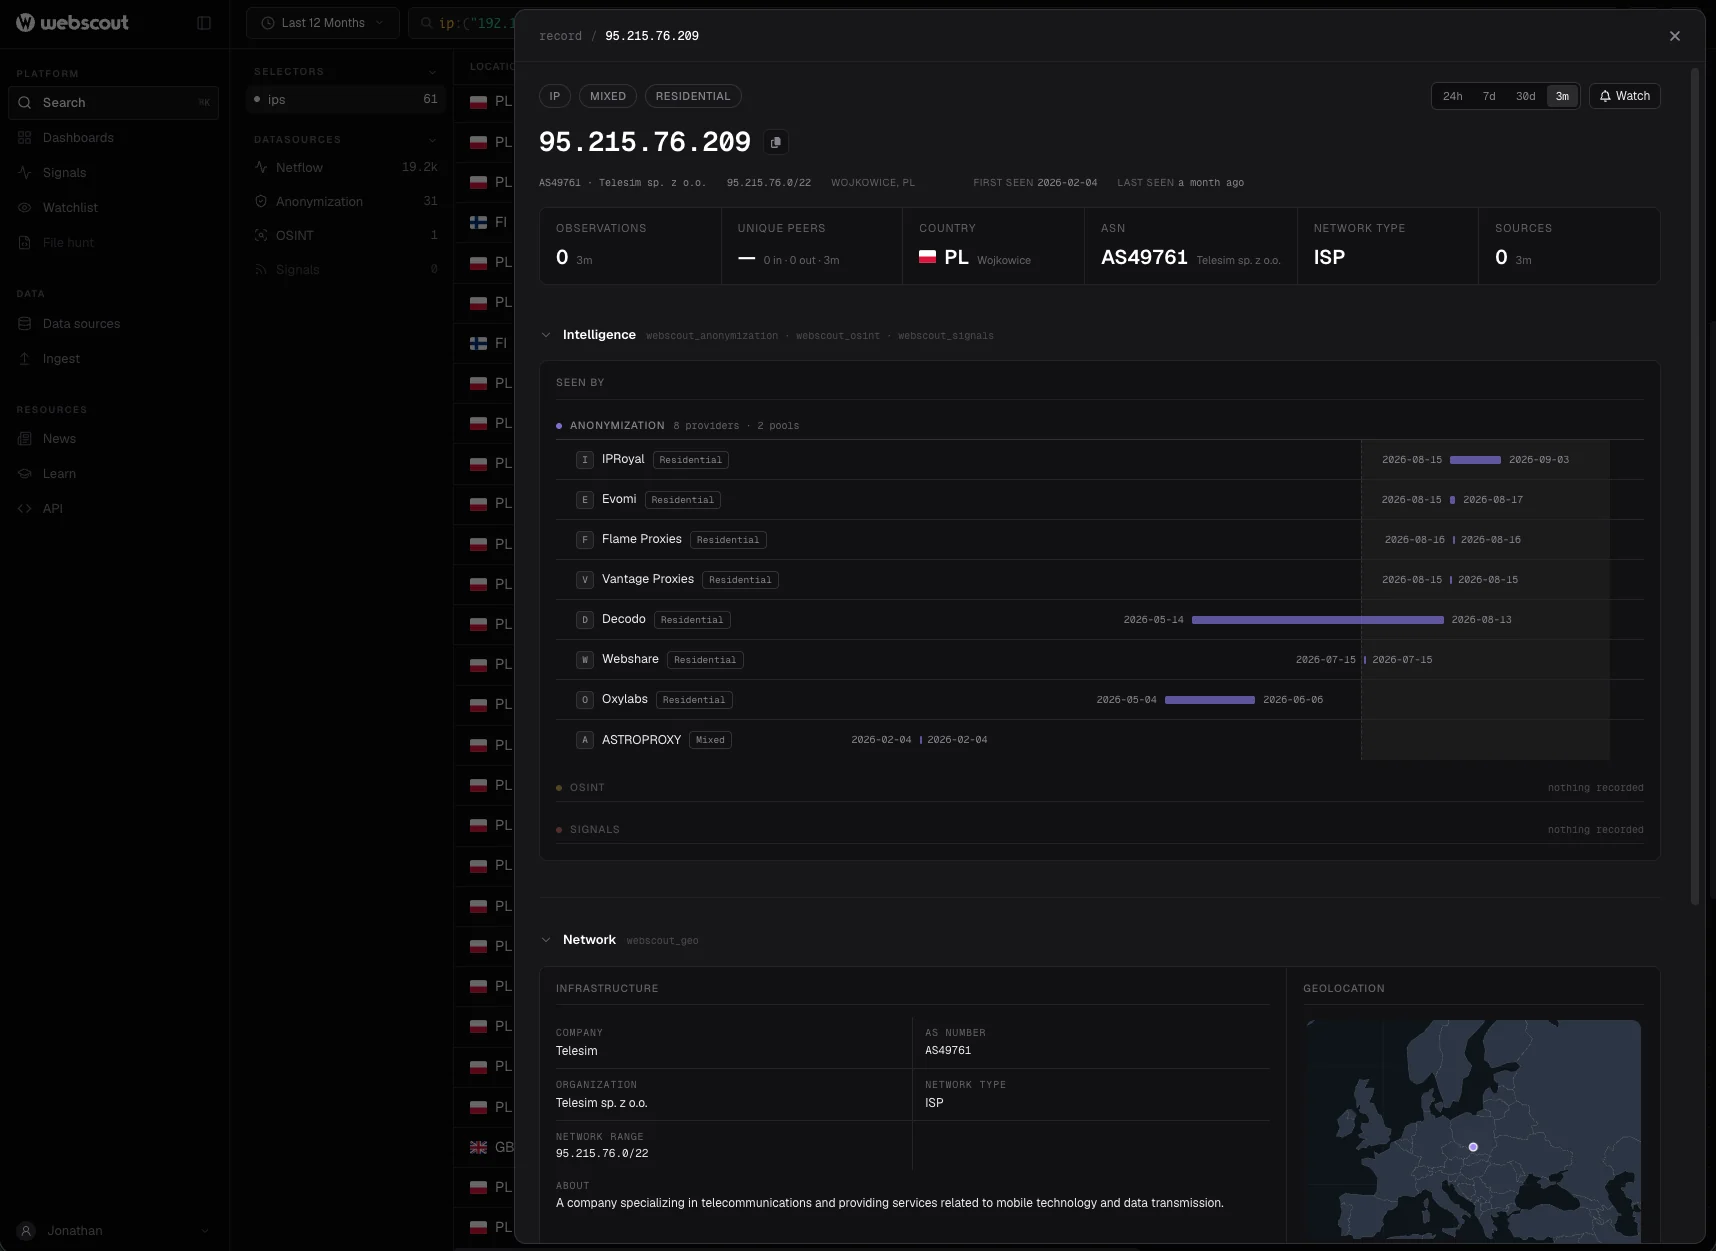
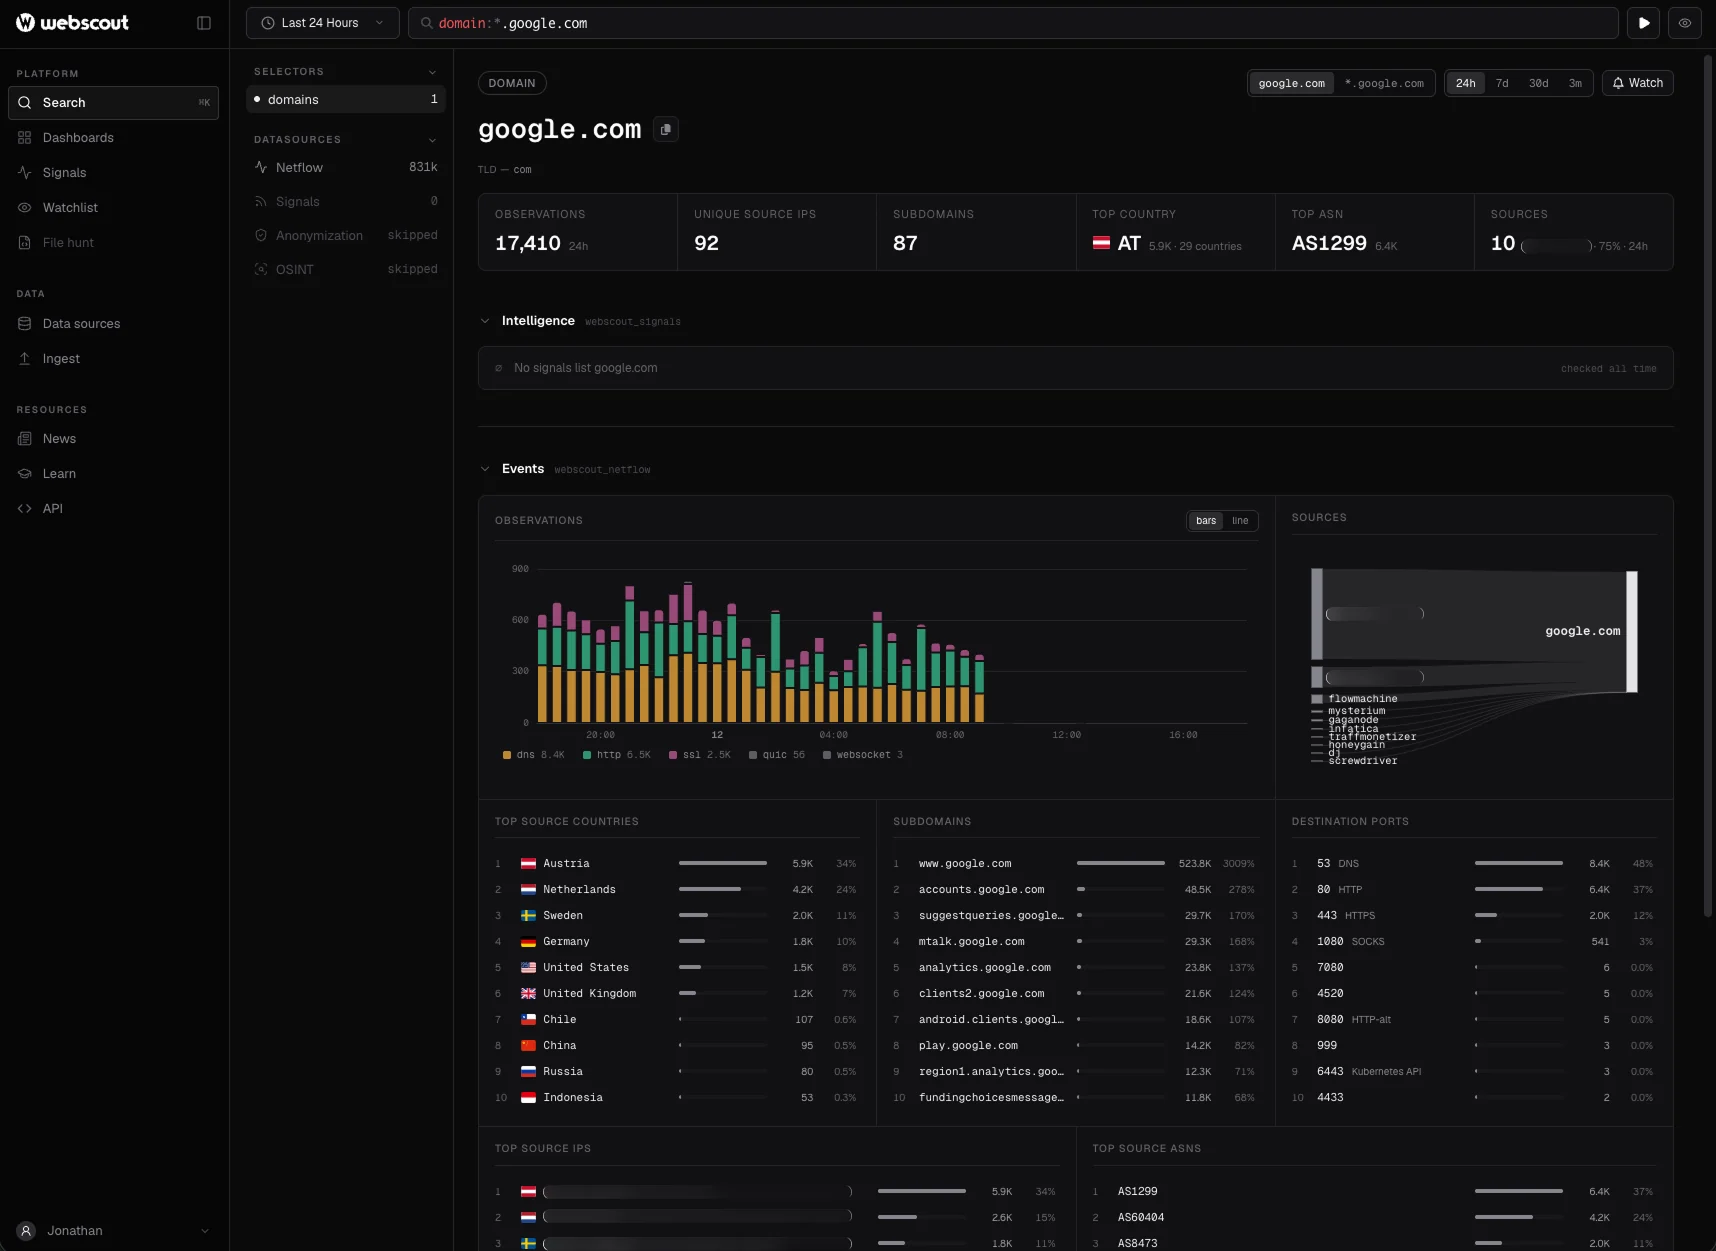
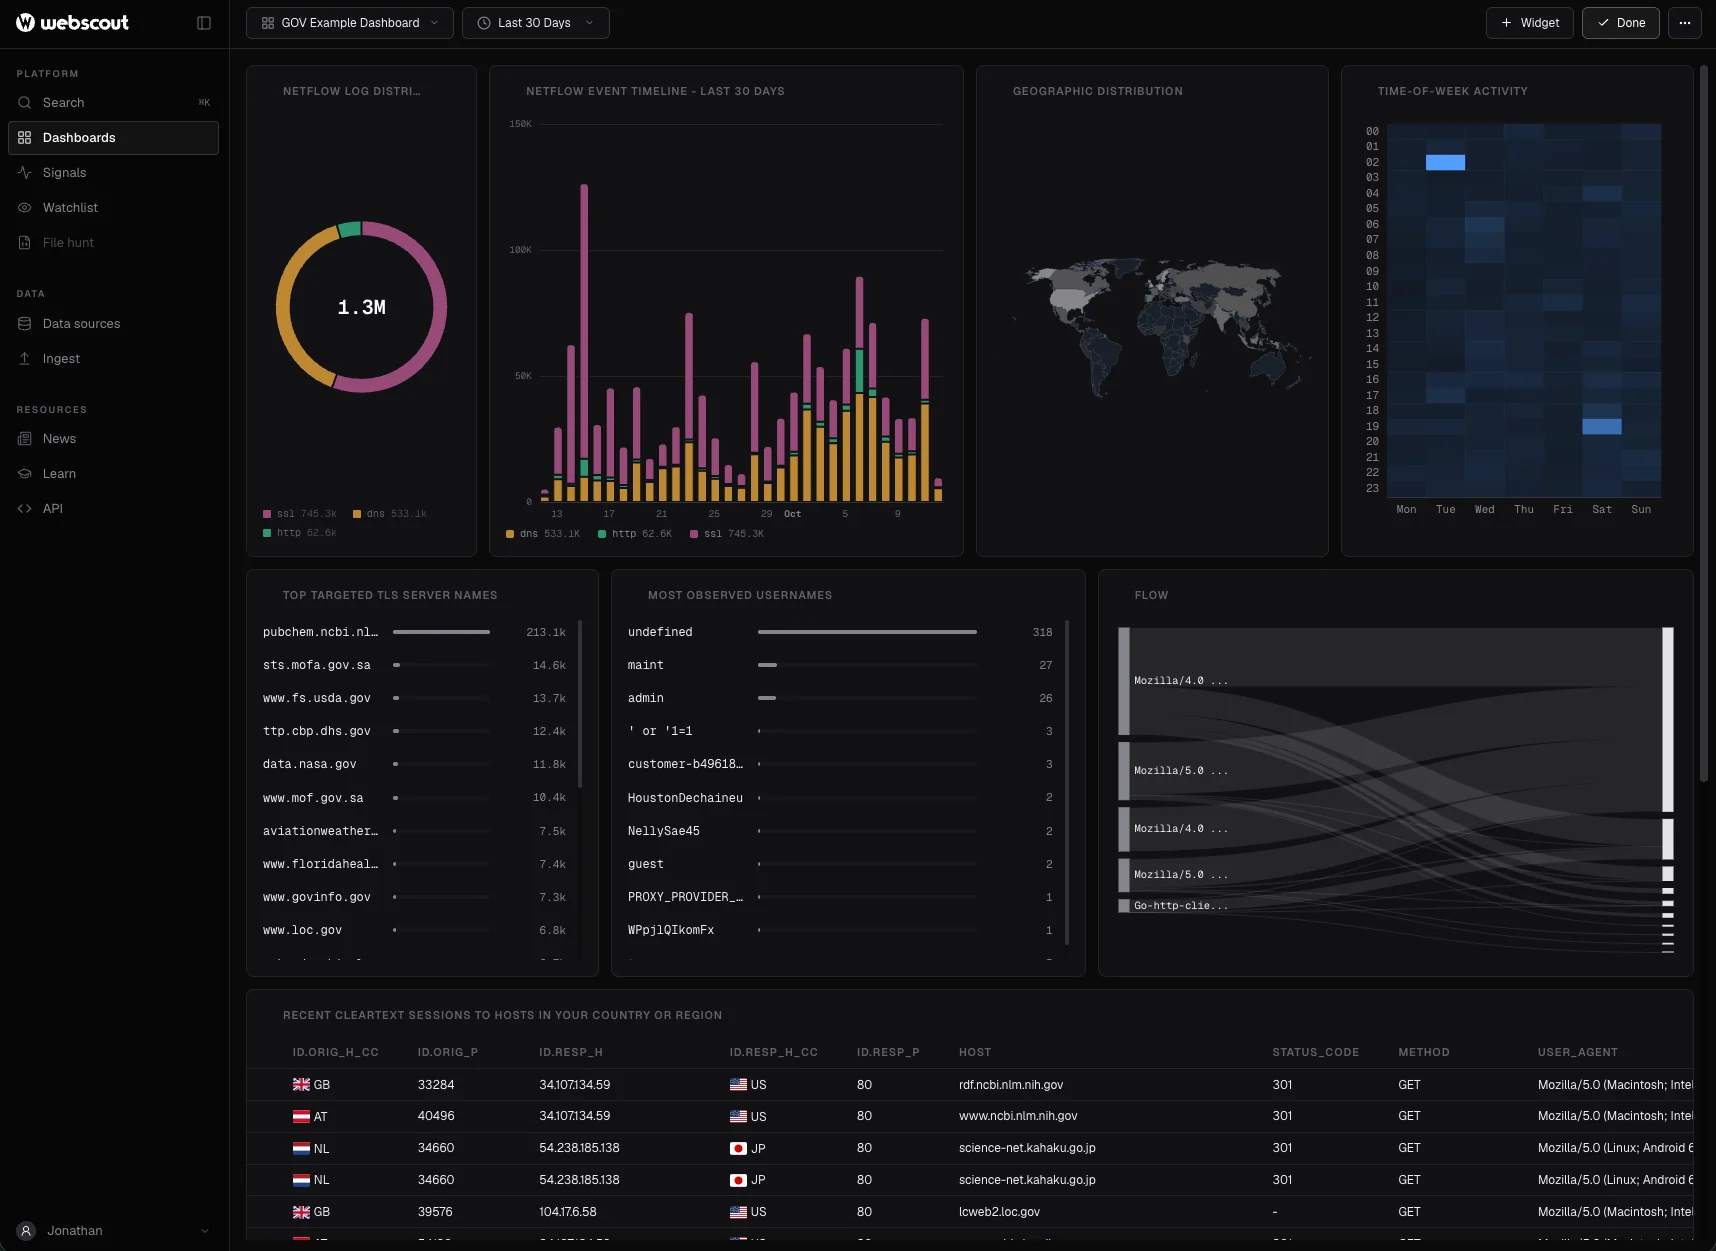
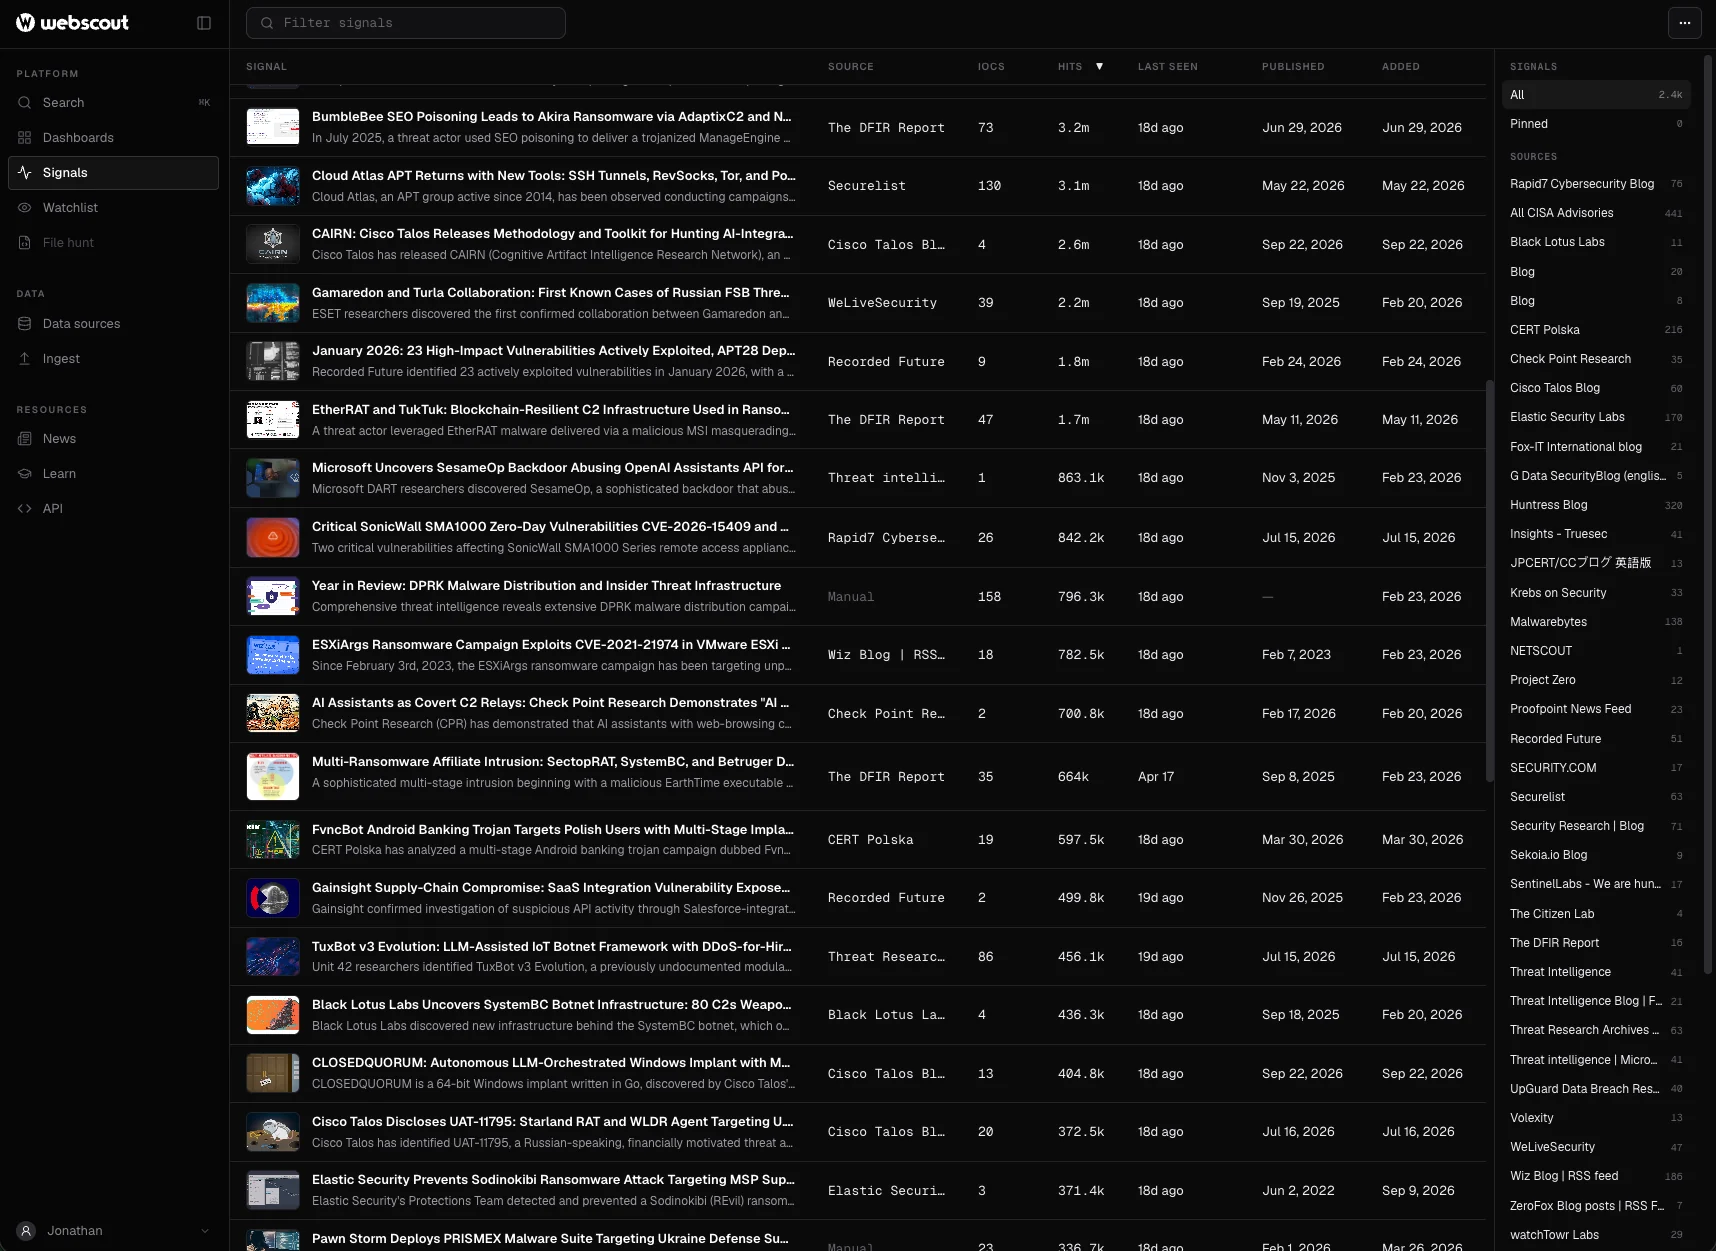
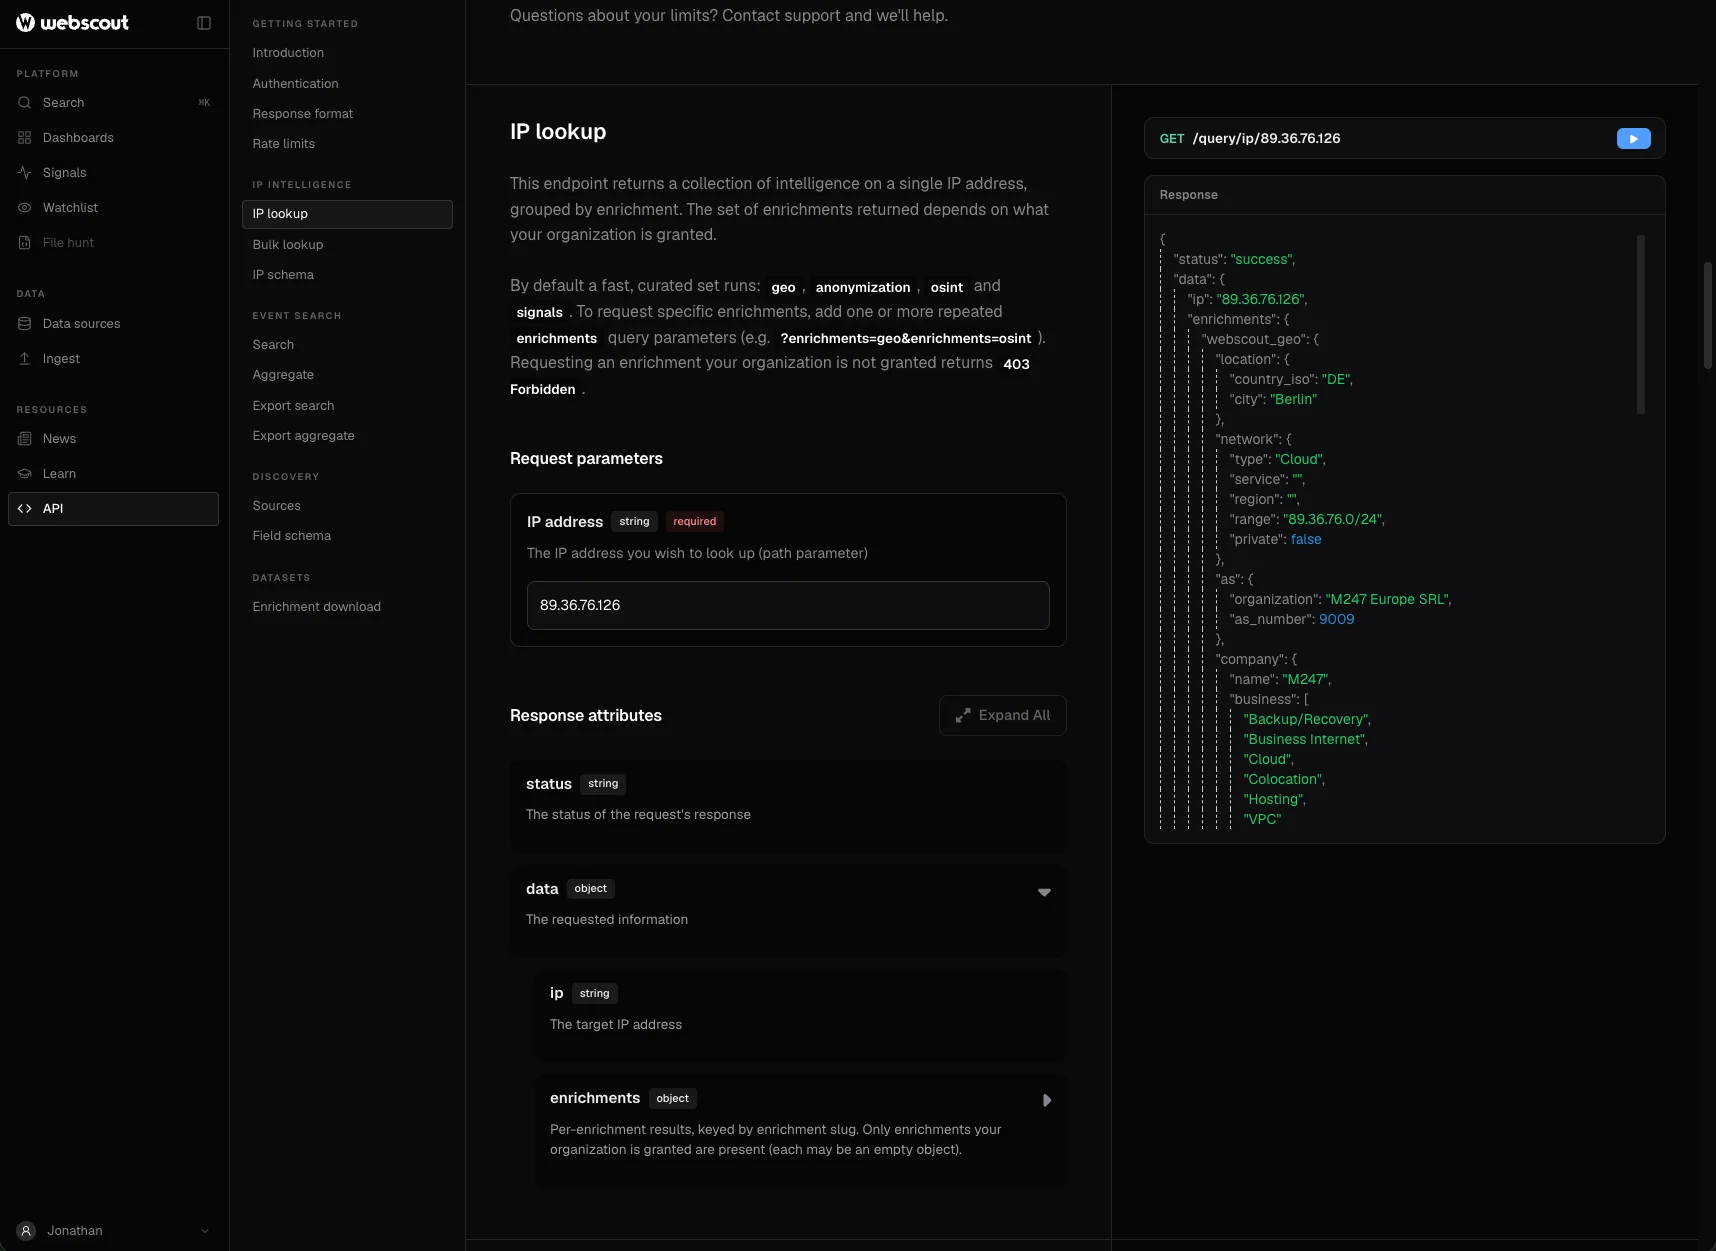
Search, aggregate and hunt across the flows in the Webscout Observability Platform, with IP context applied to every address. Flows can also be delivered via S3 for on-premises ingestion and zero-footprint deployments.
FAQ
Questions about covert network flows
What are covert networks?
The infrastructure adversaries route their operations through to hide where they come from: Tor, residential proxy networks, botnets and ORB networks of compromised devices. Traffic leaves from addresses that look unremarkable, so the target sees an ordinary connection rather than its origin.
What is an ORB network?
An operational relay box (ORB) network is a mesh of compromised devices, such as routers and IoT devices, and rented servers that threat actors, including state-sponsored groups, use to relay traffic and obscure its origin. Nodes are replaced often, so blocklists of their addresses go stale quickly. Read the guide to ORB networks.
How is an ORB network different from a botnet?
A botnet is any network of compromised devices under one controller, used for anything from denial-of-service attacks to spam. An ORB network is relay infrastructure: compromised devices, often reached through rented servers, that carry an operator’s traffic and hide where it comes from. Government advisories call them covert networks of compromised devices, also known as botnets.
Why do IP blocklists fail against covert networks?
Because the addresses do not last. A covert network can hold hundreds of thousands of devices, new nodes replace patched ones, and one group can use several networks, so indicators expire almost as fast as they are found. This is often called IOC extinction. Visibility into the networks themselves, and fingerprints that persist when addresses change, outlast any list.
What do government advisories recommend against covert networks?
The April 2026 joint advisory Defending Against China-Nexus Covert Networks of Compromised Devices, released by the UK’s NCSC with partners including CISA, the FBI, the NSA and agencies in Germany, the Netherlands, Spain and Sweden, recommends dynamic threat feeds that include covert network infrastructure, using flow data to look upstream and map covert networks, and tracking covert networks as threats in their own right. Covert network flows provides flows from inside those networks for that work.
How does Webscout see covert network traffic?
Through its own sensors inside covert networks. Webscout observes the flows that pass through anonymising infrastructure, more than 1.5 billion events a day, with JA4+ fingerprints and IP context on every connection.
Can I see who is targeting my organisation?
Yes. Search the flows for your own address ranges to see who reaches them through covert networks, including activity that never shows up in your own perimeter logs.
How is the data delivered?
In the Webscout Observability Platform, where you search, aggregate and hunt with IP context on every address, or via S3 for on-premises ingestion and zero-footprint deployments.
Who can access covert network flows?
Only vetted government partners.
Webscout works exclusively with vetted partners in government, defence, intelligence and critical infrastructure.Contact info@webscout.io to learn more.