SolutionsPlatform
Webscout Observability Platform
The hub for full-stack network detection, response and intelligence. Your telemetry, Webscout’s covert network traffic, or both, side by side in one interface.
Live on app.webscout.io
One hub
Your telemetry, Webscout’s covert traffic, or both, side by side in one place
One hub for network detection, response and intelligence. Search, correlate and hunt across everything you connect.
Proprietary sources and proprietary enrichments, built for defence and intelligence work.
Inside the platform
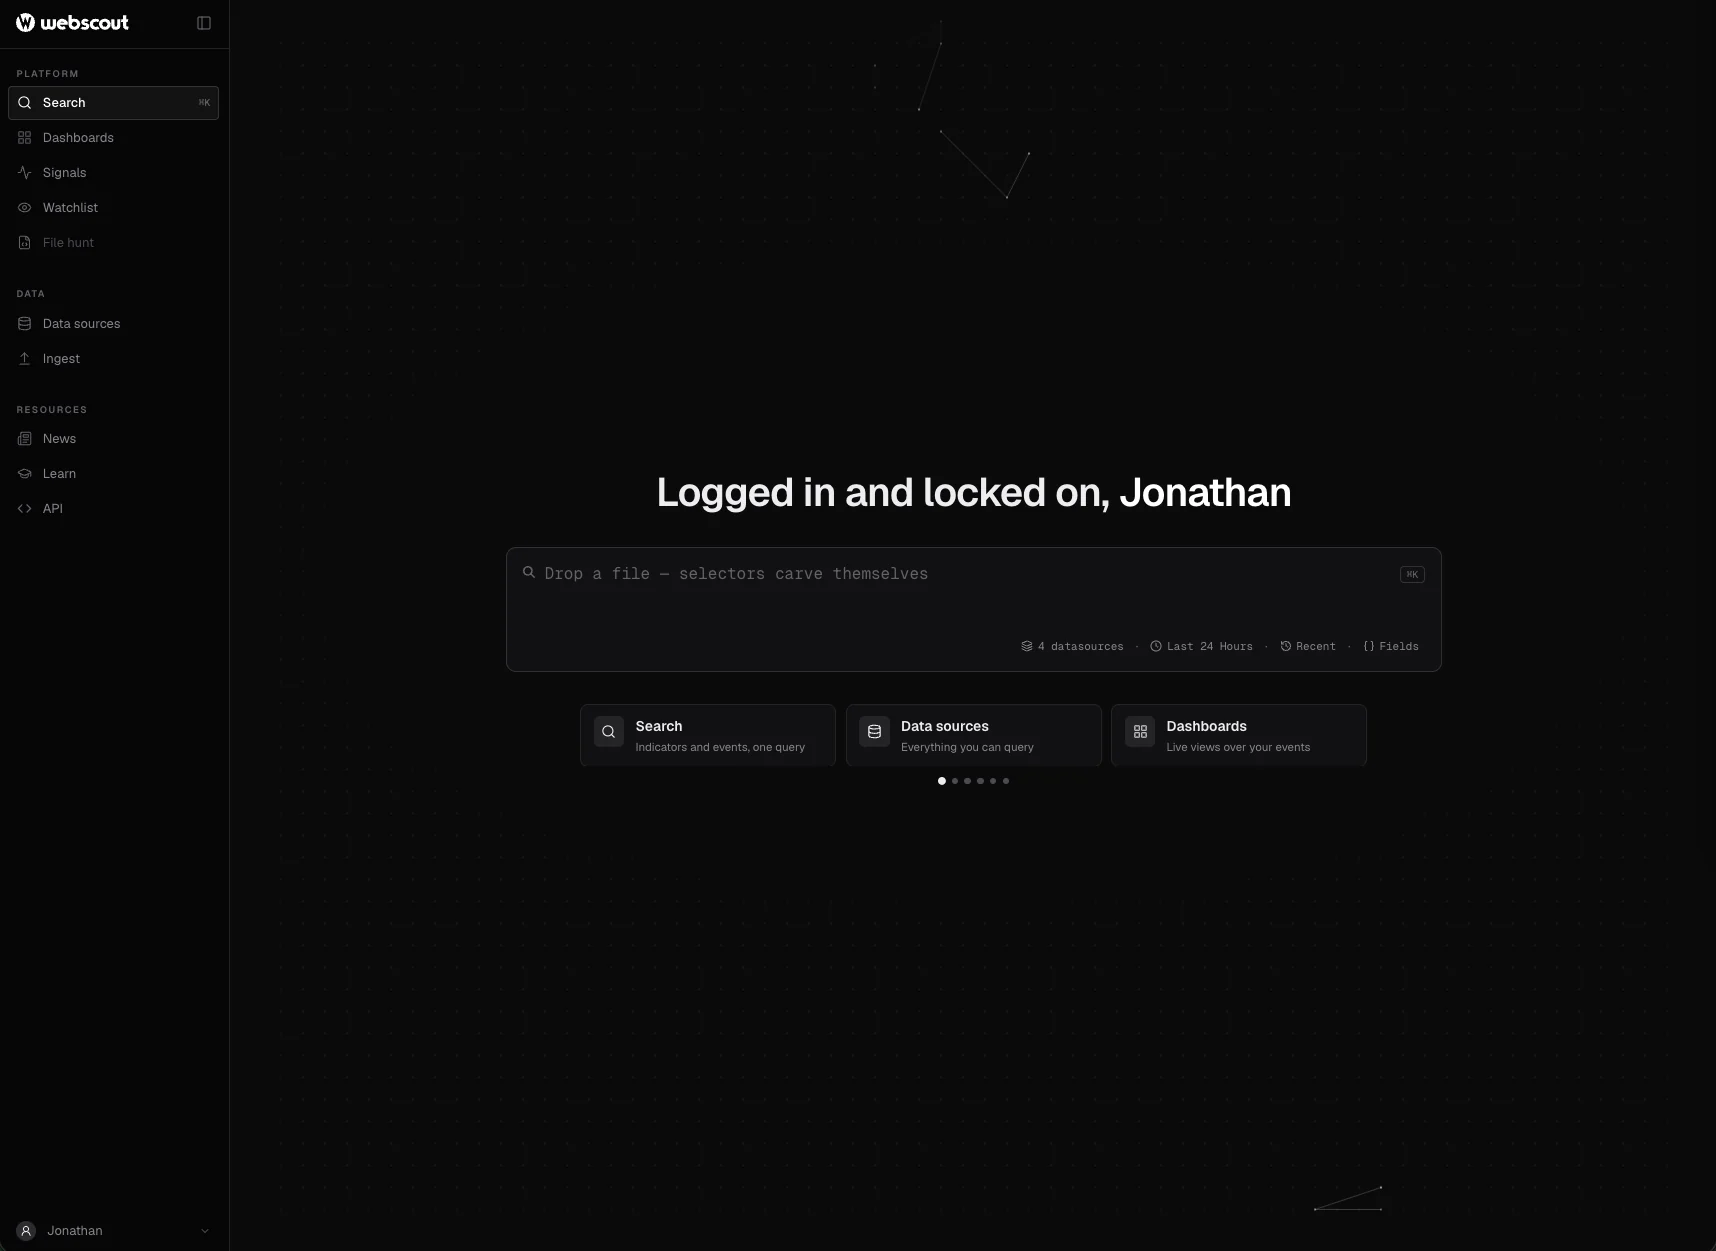
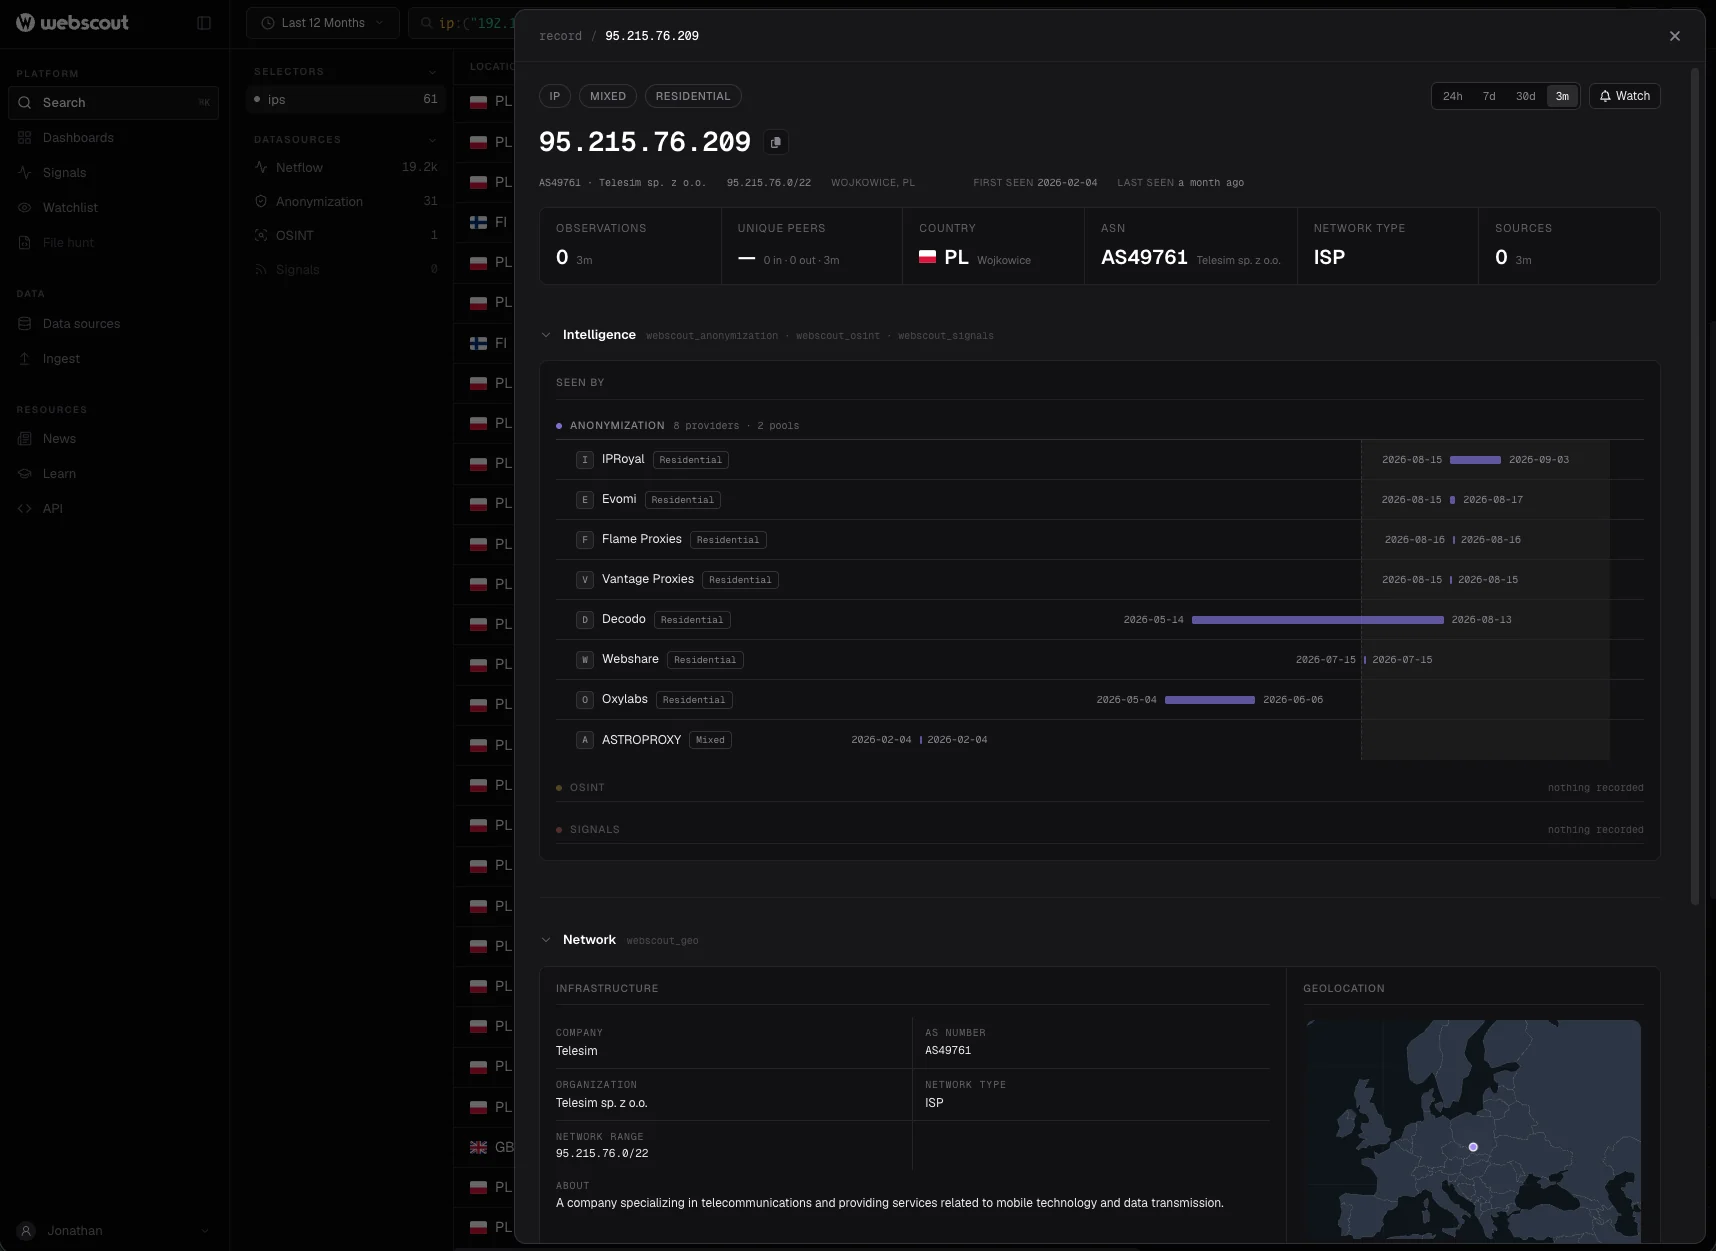
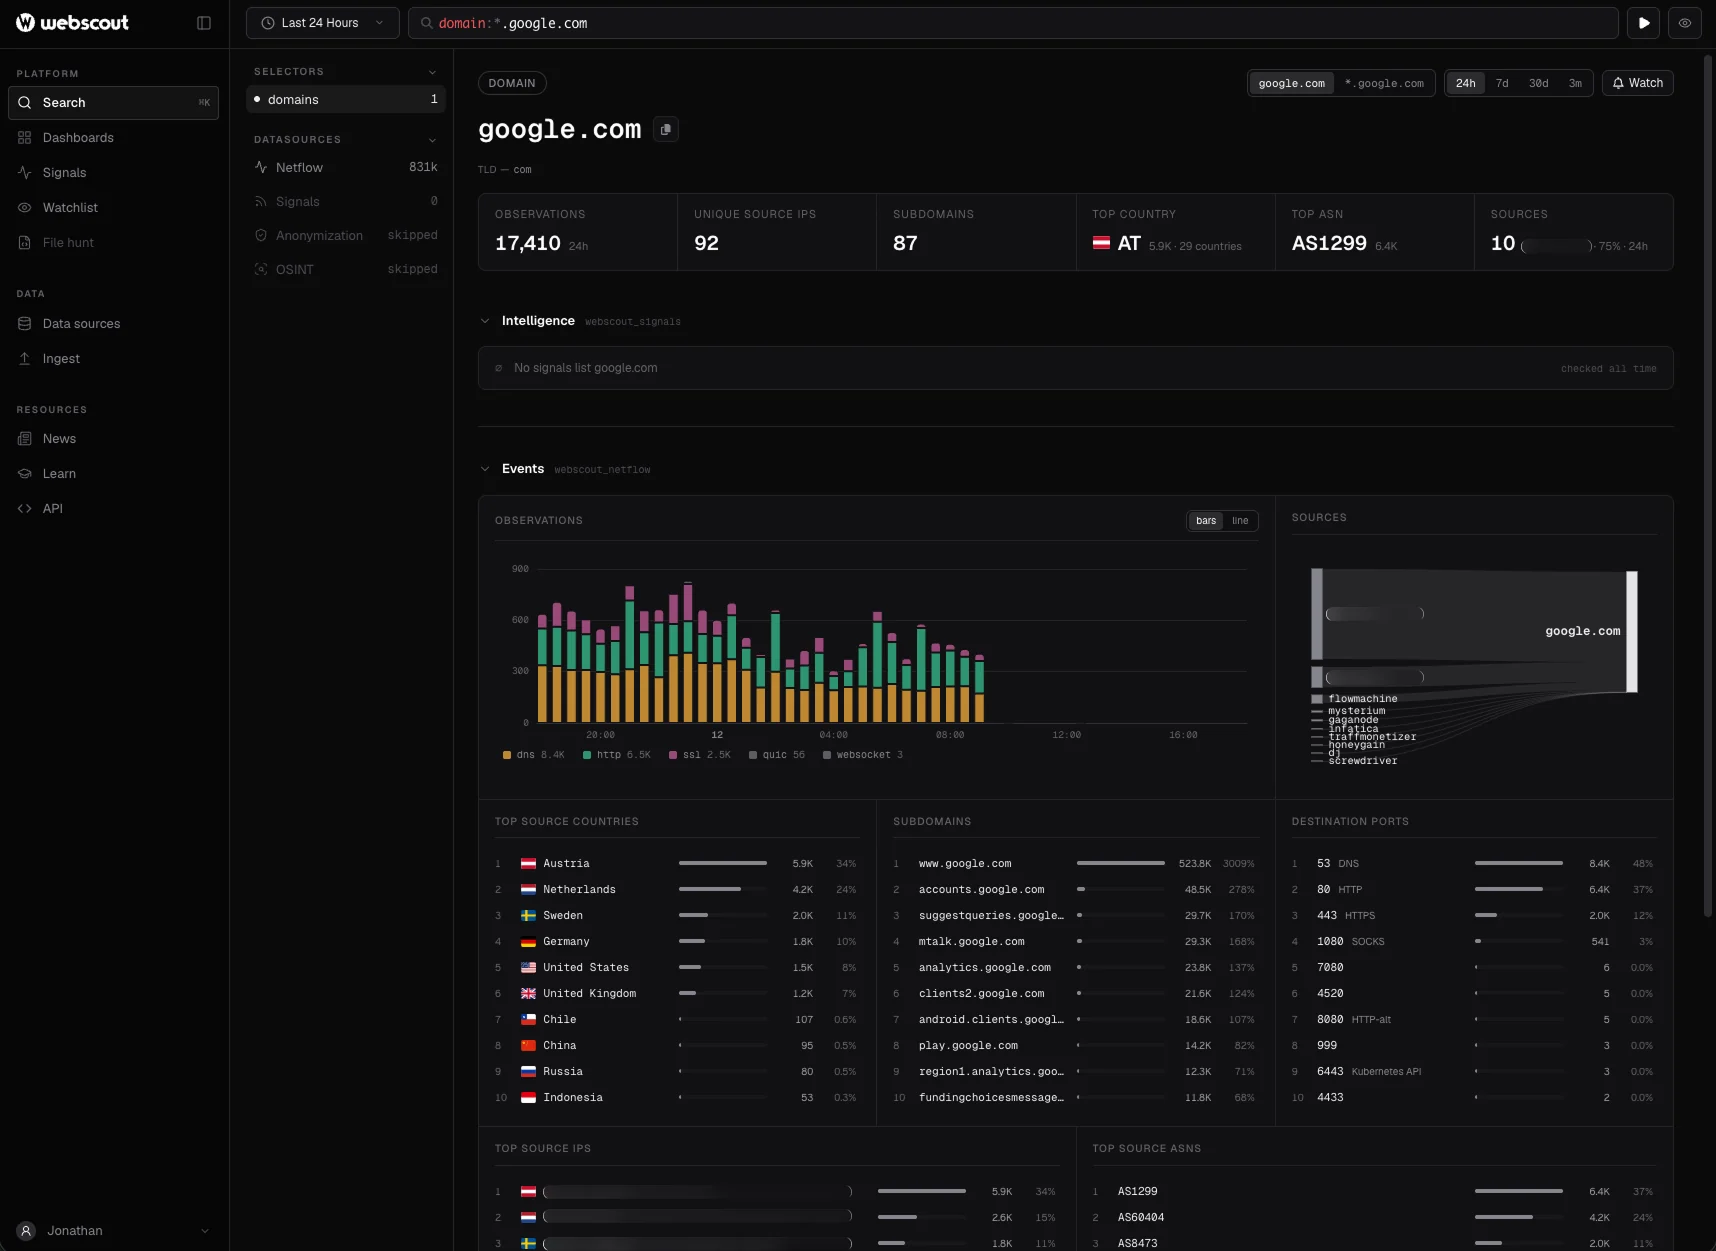
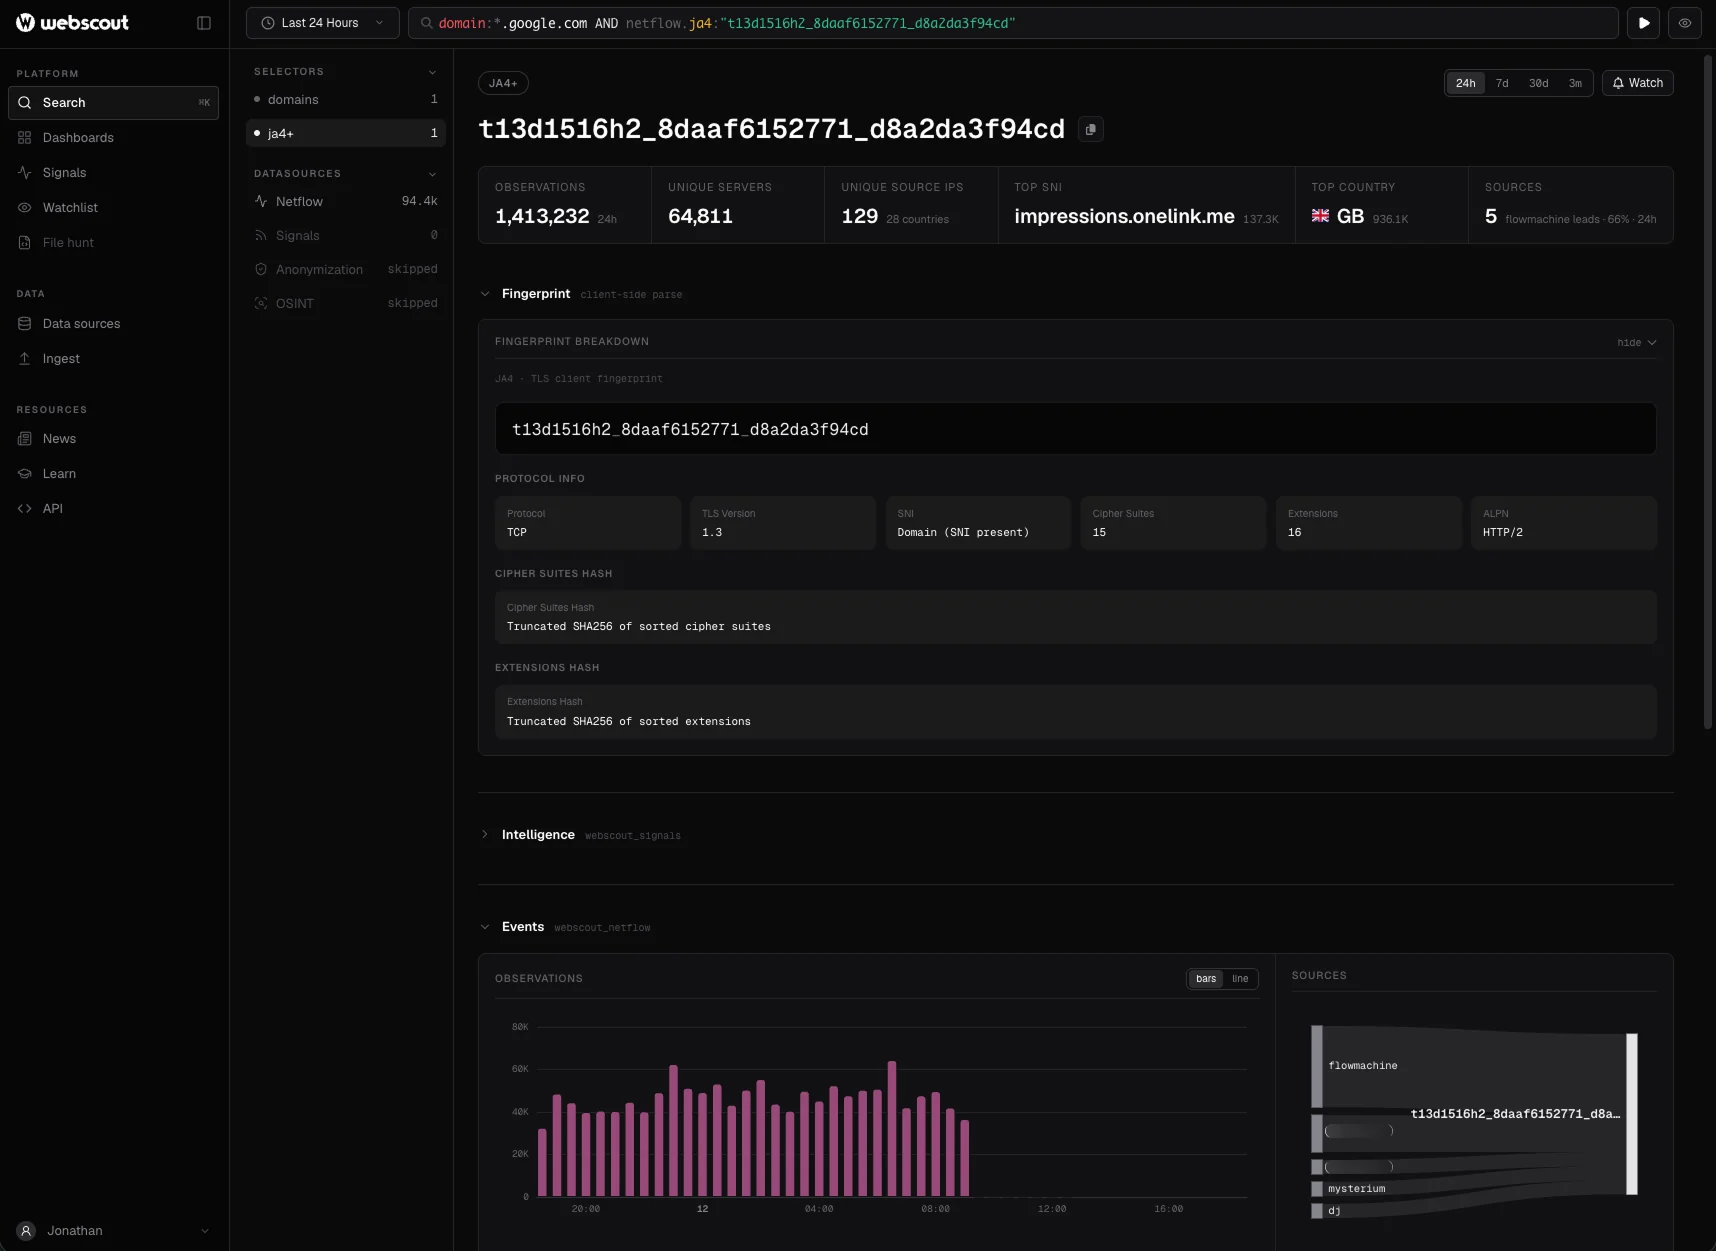
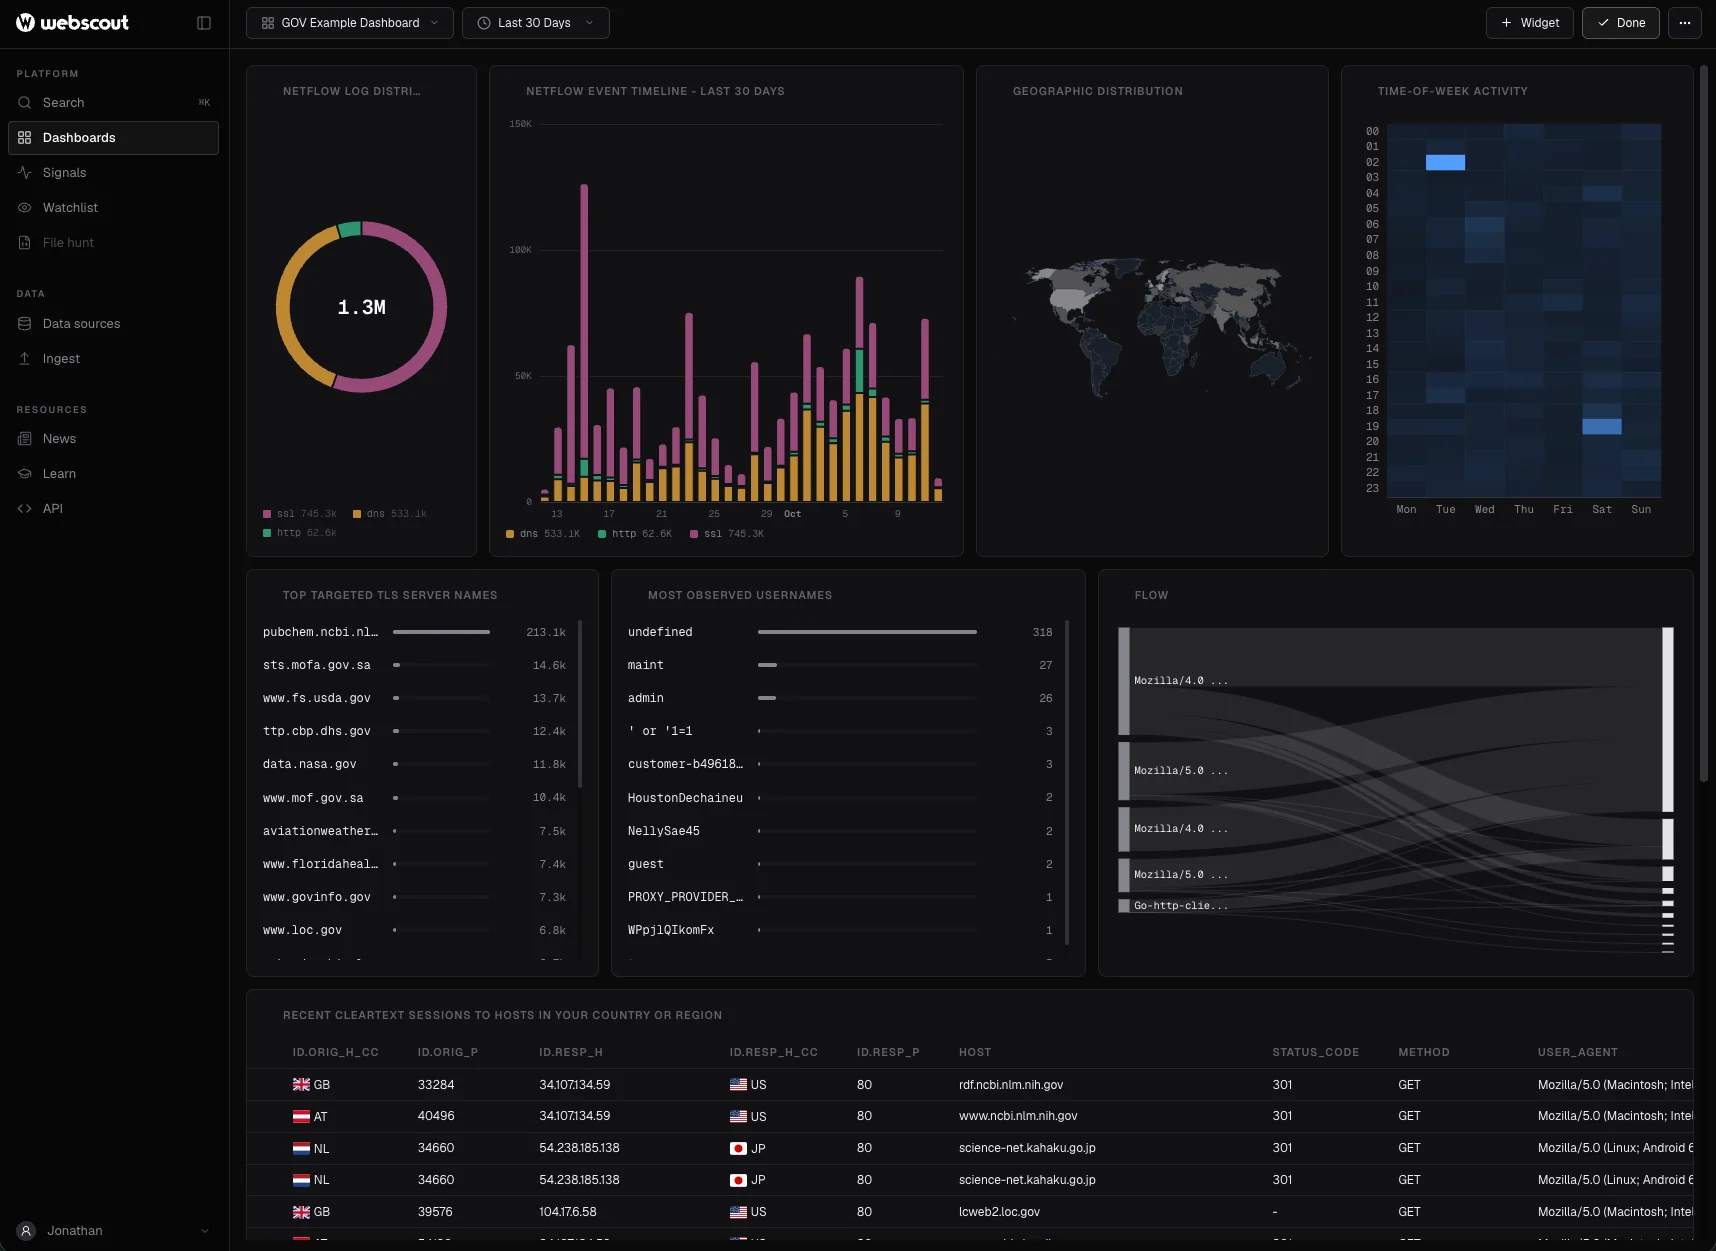
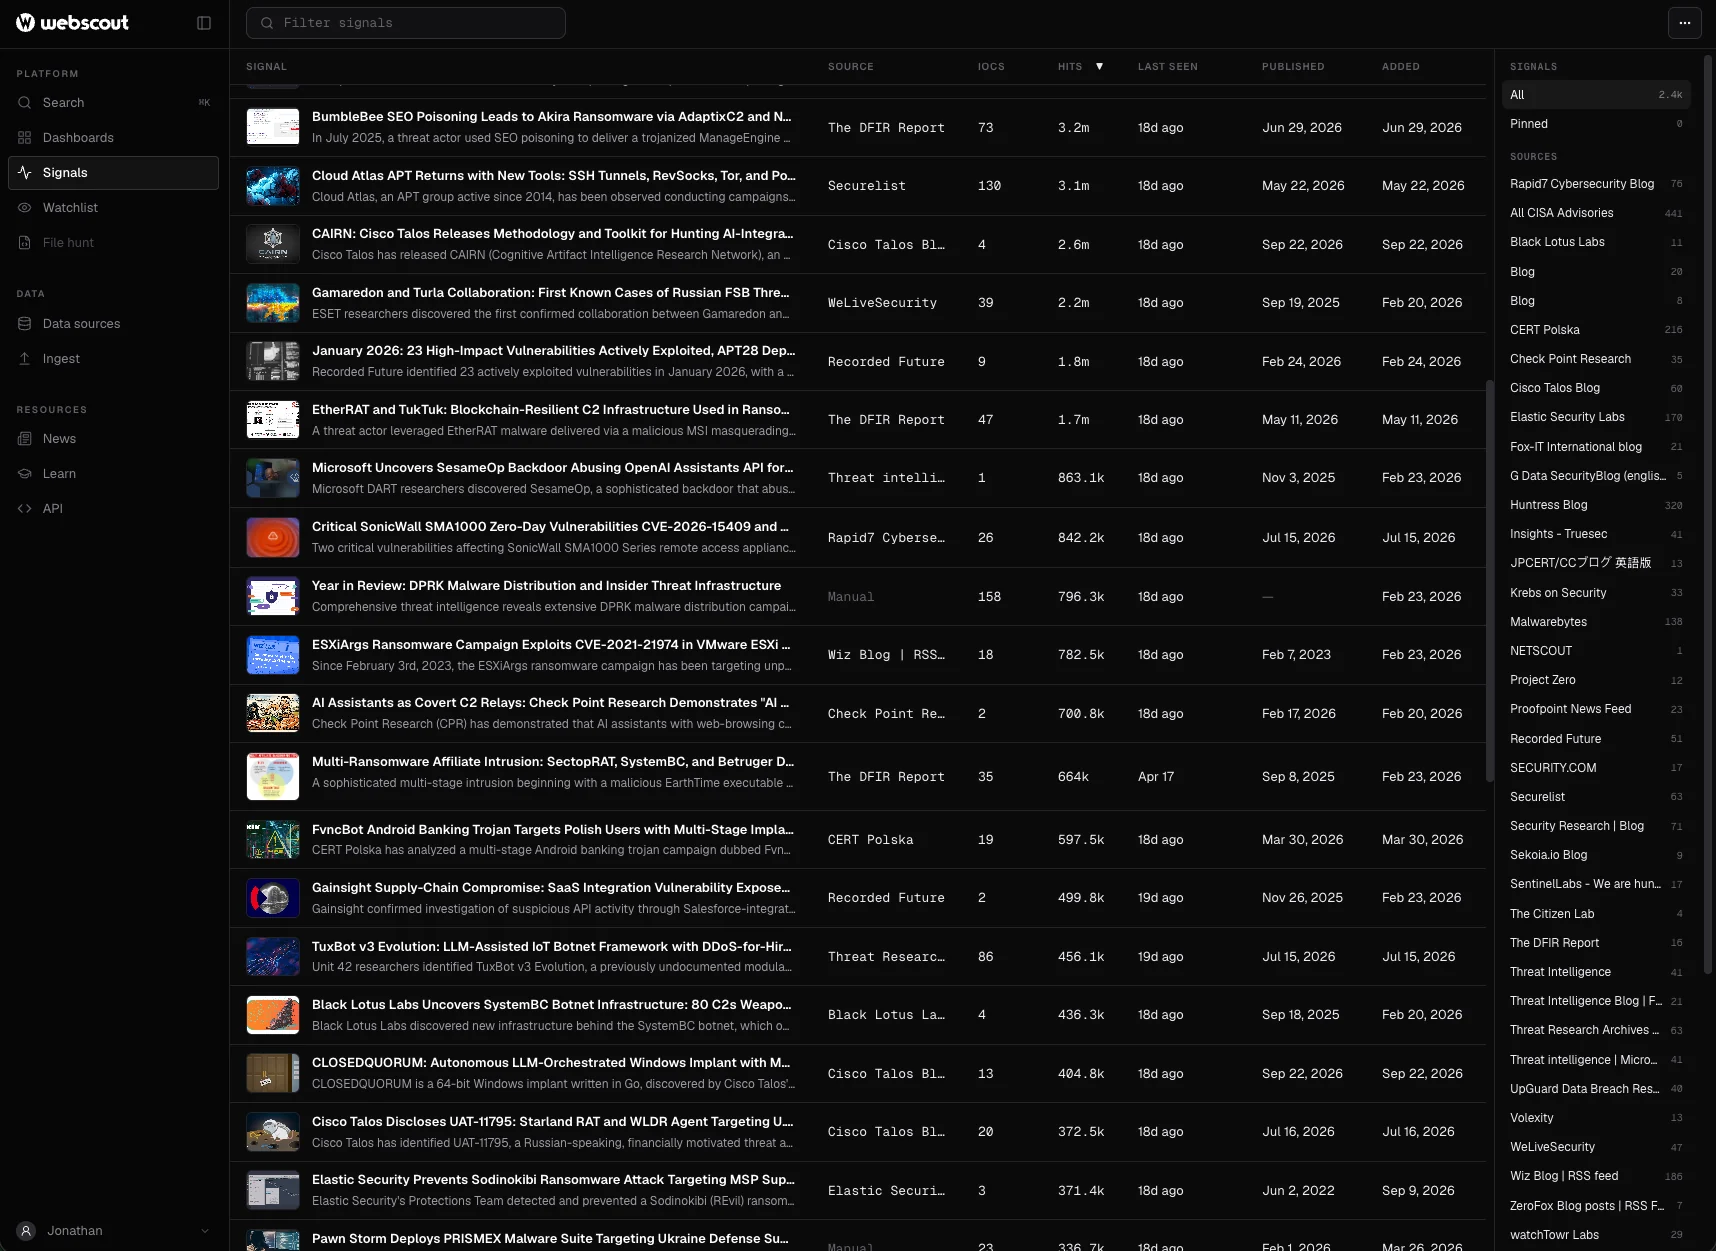
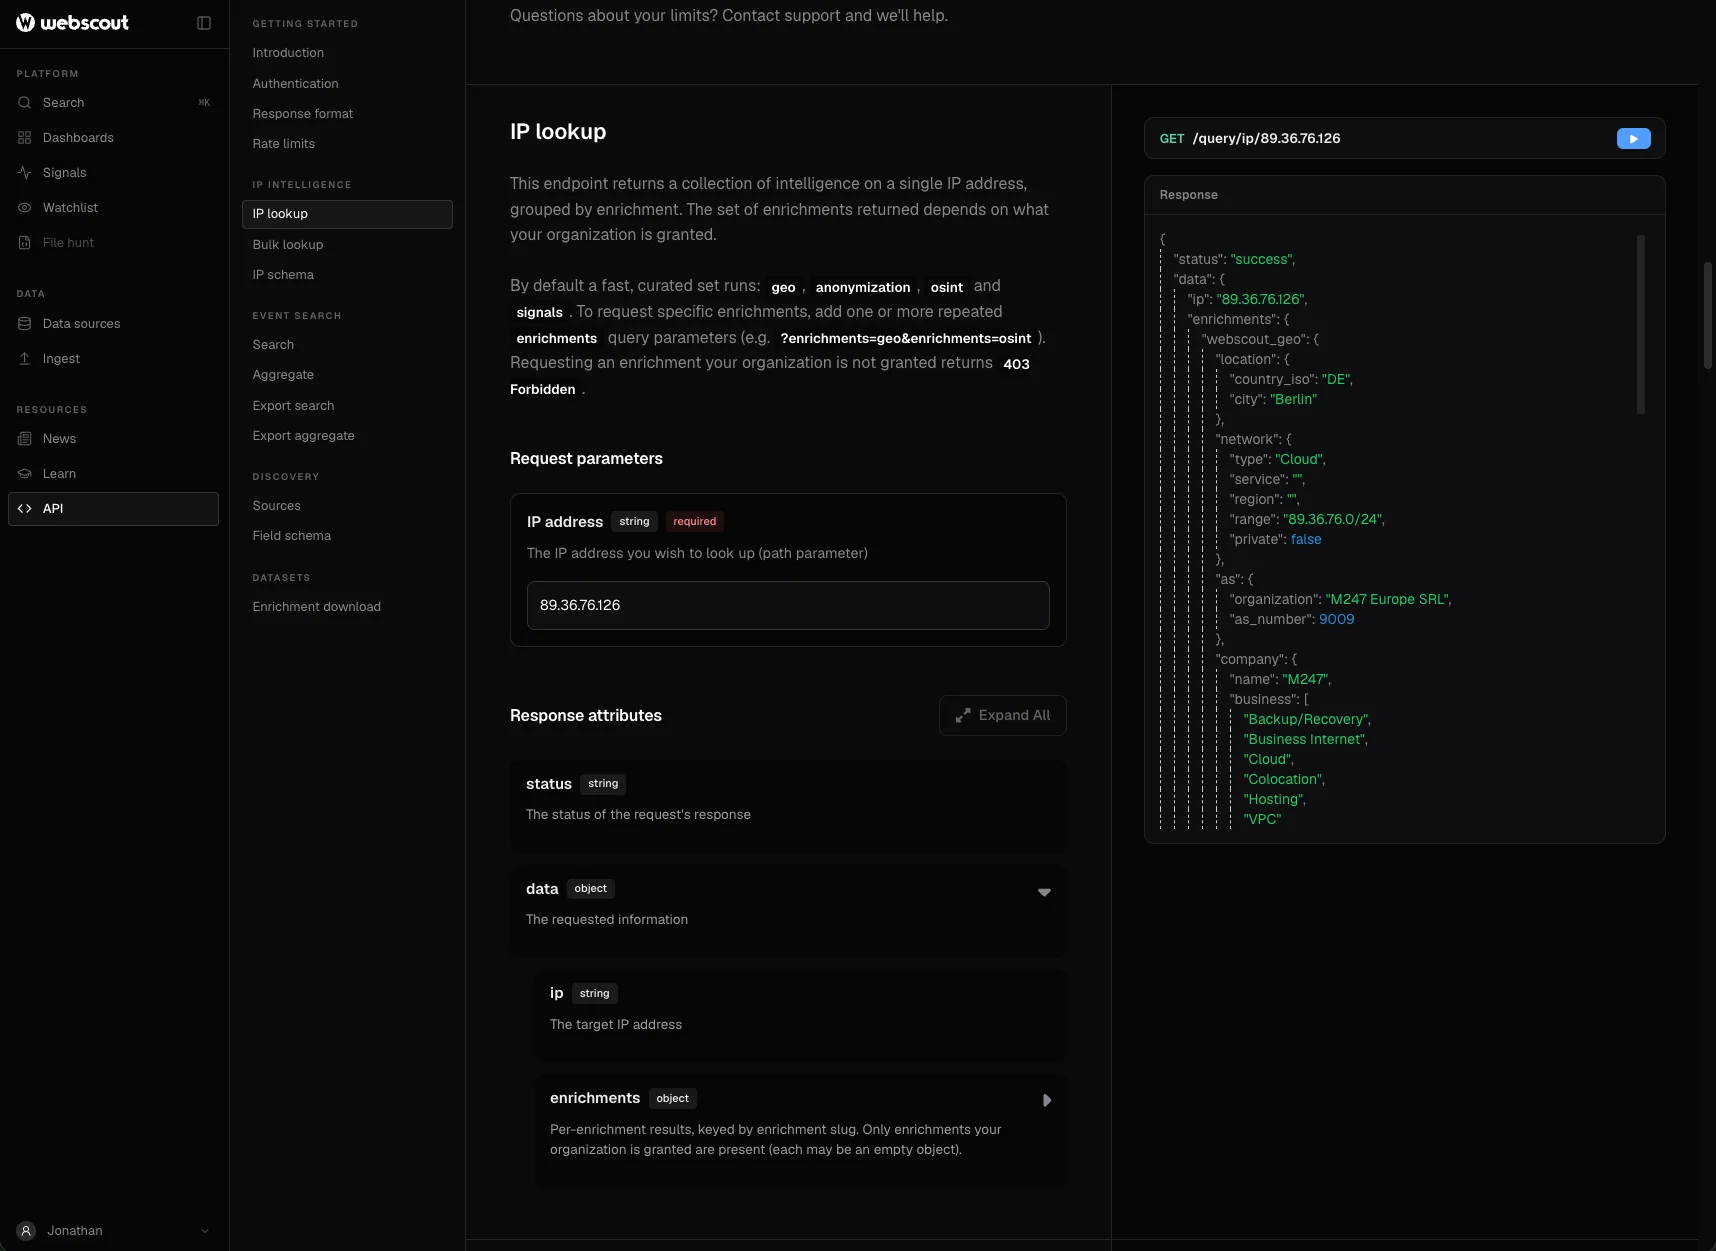
Search, investigate and respond in one interface
Lookups for every IP, domain and JA4+ fingerprint, dashboards over your events, and signals curated from published threat reporting, with their hits in your data.
Sources
Start with your telemetry, extend it with ours
Connect what you already run, and add Webscout’s enrichments and covert network traffic where you need more. Everything sits side by side in the same searches.
01
Your telemetry and enrichments
Connect your own sources and the enrichments of your choice. The platform contextualises, correlates and searches them in one place.
- Zeek logs, cloud logs, PCAP, web logs and firewall flows
- Partner feeds and lawful intercept data
- Third-party enrichments and intelligence through APIs and data feeds
02
Webscout’s enrichments and covert traffic
Batteries included. Webscout’s proprietary enrichments on every IP, and covert network traffic as an extension of what your sensors see.
- Anonymisation, residential proxy, geo and network enrichment on every IP
- JA4+ fingerprints and curated signals
- Covert network flows, honeypot flows from Webscout’s global honeypot mesh, and Webscout sensor data
What it does
From the alert to the investigation behind it
01
High-speed search
Lucene queries across connection, DNS, HTTP and other log types, with a time histogram and log-type distribution for every query.
02
Automatic contextualisation
Every IP in context, from geolocation and network ownership to VPN, Tor and residential proxy attribution, in every search, lookup and investigation.
Anonymising IPs03
Aggregate and correlate
Top values, unique counts, significant terms and histograms, without pulling the underlying events.
04
Pivot on any selector
Move across related infrastructure from an IP, domain, URL, JA4+ fingerprint, hash, email, ASN or country.
05
Dashboards and signals
Live views over your events and curated network signals, for alerting and detection.
06
Results where you need them
Stream results and aggregations to JSONL or CSV, or pull them over the API into your SIEM or MISP.
Use cases
Detection, response and intelligence, in one place
01
Threat hunting
Start from a JA4+ fingerprint, an ASN or a residential proxy provider and see every matching connection across your connection, DNS, HTTP and other logs, then pivot from there.
02
Incident response and network forensics
Reconstruct an incident from the network record: which hosts talked to which infrastructure, when, and through which anonymising service, from the Zeek logs, PCAP and flows you already collect.
03
Detection engineering
Turn findings into custom rulesets and alerts, and watch signals curated from published threat reporting hit your own data.
04
NDR and SIEM work in one interface
Detection on your network telemetry and high-speed search, correlation and dashboards across your logs, so analysts detect, investigate and respond in the same place.
Deployment
Run it where your mission requires
01
Cloud
Operated by Webscout in a sovereign European cloud and reached from your browser.
- Live on app.webscout.io
- Web interface and REST API
- Access per vetted organisation
02
On-premises
Sovereign deployment on your premises, so sensitive network data and investigative workflows stay within your environment.
- Local ingestion of your own telemetry
- Air-gapped for select partners in high-side environments
- Containerised and standalone, for zero-footprint operations
FAQ
Questions about the platform
Can I bring my existing Zeek logs, PCAP and flows?
Yes. Connect your own network telemetry, such as Zeek logs, cloud logs, PCAP, web logs and firewall flows, plus partner feeds, lawful intercept data and third-party enrichments through APIs and data feeds. Webscout’s covert network flows, honeypot flows and enrichments sit beside them in the same searches.
How is it different from a network detection and response (NDR) tool?
On your own networks it works like an NDR, with every connection in context. It then adds what your sensors cannot see: Webscout’s covert network traffic from Tor, residential proxies and ORB networks, and VPN, Tor and residential proxy attribution for every IP address.
Does it replace a SIEM?
It brings NDR- and SIEM-class capability into one interface: detection on your network telemetry, and high-speed search, correlation and dashboards across your logs. It can also run beside an existing SIEM, with results and aggregations sent there over the REST API or as JSONL or CSV.
How are VPN, Tor and residential proxy connections identified?
Every IP address in every event is matched against Webscout’s anonymisation dataset, which names the VPN or proxy provider behind it, or marks it as a Tor relay, with the kind of pool and when it was seen. Geolocation and network ownership are added the same way.
How does it handle encrypted traffic?
Through JA4+ fingerprints, which characterise the client and server software from the TLS handshake, and from HTTP, SSH and TCP. Encrypted sessions can be grouped, searched and pivoted on without decrypting them.
Can it run on-premises or air-gapped?
Yes. Use the cloud version, operated by Webscout in a sovereign European cloud, or run it on your premises: containerised and standalone, with local ingestion of your own telemetry. Air-gapped deployments are available for select partners in high-side environments. See air-gapped network analysis.
Where is our data held?
In the cloud version, in a sovereign European cloud operated by Webscout, with access per vetted organisation. On premises, in your own environment: sensitive network data and investigative workflows stay there.
How do analysts search and investigate?
With high-speed Lucene search across connection, DNS, HTTP and other log types, aggregations such as top values, unique counts and significant terms, and pivots on any selector: IP address, domain, URL, JA4+ fingerprint, hash, email, ASN or country. See threat hunting in Zeek logs.
Does it support JA4+ fingerprints?
Natively. JA4+ fingerprints are carried on flows and can be searched and pivoted on, and JA4DB, built on the platform, returns the context behind any fingerprint. See JA4+ fingerprints explained.
Can results go to our SIEM or MISP?
Yes. Stream results and aggregations to JSONL or CSV, or pull them over the REST API into your SIEM, MISP or other tools.
Who can use the platform?
Webscout works exclusively with vetted partners in government, defence, intelligence and critical infrastructure. Contact info@webscout.io to learn more.
Webscout works exclusively with vetted partners in government, defence, intelligence and critical infrastructure.Contact info@webscout.io to learn more.